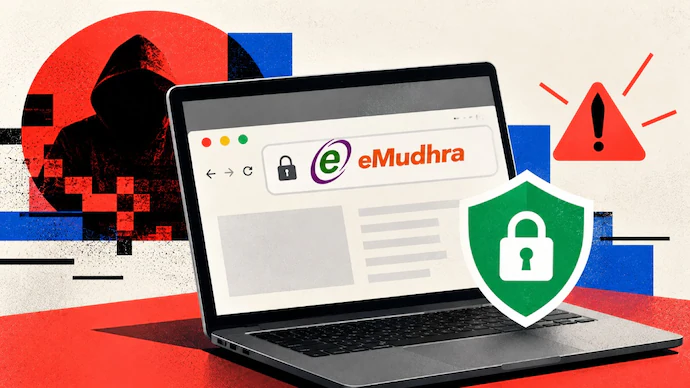
Digital trust services provider eMudhra will voluntarily withdraw from the global SSL/TLS certificate business following a security incident involving compromised private keys.
The company announced the decision on Thursday, a day after disclosing that private keys associated with its certificates had been compromised. The incident affected a limited part of its global Transport Layer Security (TLS) business, eMudhra said.
An advisory from India’s cybersecurity watchdog, the Indian Computer Emergency Response Team (CERT-In), also flagged the compromise, according to the information reported.
eMudhra said the incident had no connection with its Indian Digital Signature Certificate (DSC) and eSign businesses. The company maintained that the impact was limited to its global TLS operations.
eMudhra SSL/TLS certificate business affected by security incident
SSL/TLS certificates help establish trust between websites and users by enabling encrypted connections. They are commonly associated with HTTPS websites and help protect data exchanged between browsers, applications and online services.
Private keys are a critical component of public key infrastructure (PKI). If compromised, they can undermine the trust associated with digital certificates and create security risks, depending on the circumstances and scope of the exposure.
PKI uses public and private key pairs, digital certificates and related systems to support encryption, authentication and secure digital transactions.
eMudhra provides digital trust services, including certificates used for digital signatures across online transactions. Its decision to exit the global SSL/TLS certificate business follows the reported compromise involving certificates issued through its global operations.
The company has not indicated in the supplied statement that its Indian DSC and eSign businesses were affected. It specifically separated those operations from the incident involving its global TLS business.
Indian digital signature and eSign services remain unaffected
eMudhra said its Indian Digital Signature Certificate and eSign businesses were not connected to the incident.
Digital Signature Certificates are used to authenticate signatories and support digitally signed documents and transactions. eSign services enable electronic signing through digital processes.
The distinction is significant because TLS certificates and digital signature services serve different purposes, even though both rely on digital trust infrastructure.
The company’s voluntary withdrawal concerns its global SSL/TLS certificate business. The available information does not specify a timeline for the withdrawal or provide further details about the number of certificates affected.
The incident highlights the importance of protecting private keys and maintaining the integrity of digital certificate systems, which underpin secure online communication and authentication.